
MSR with reverse proxy
-
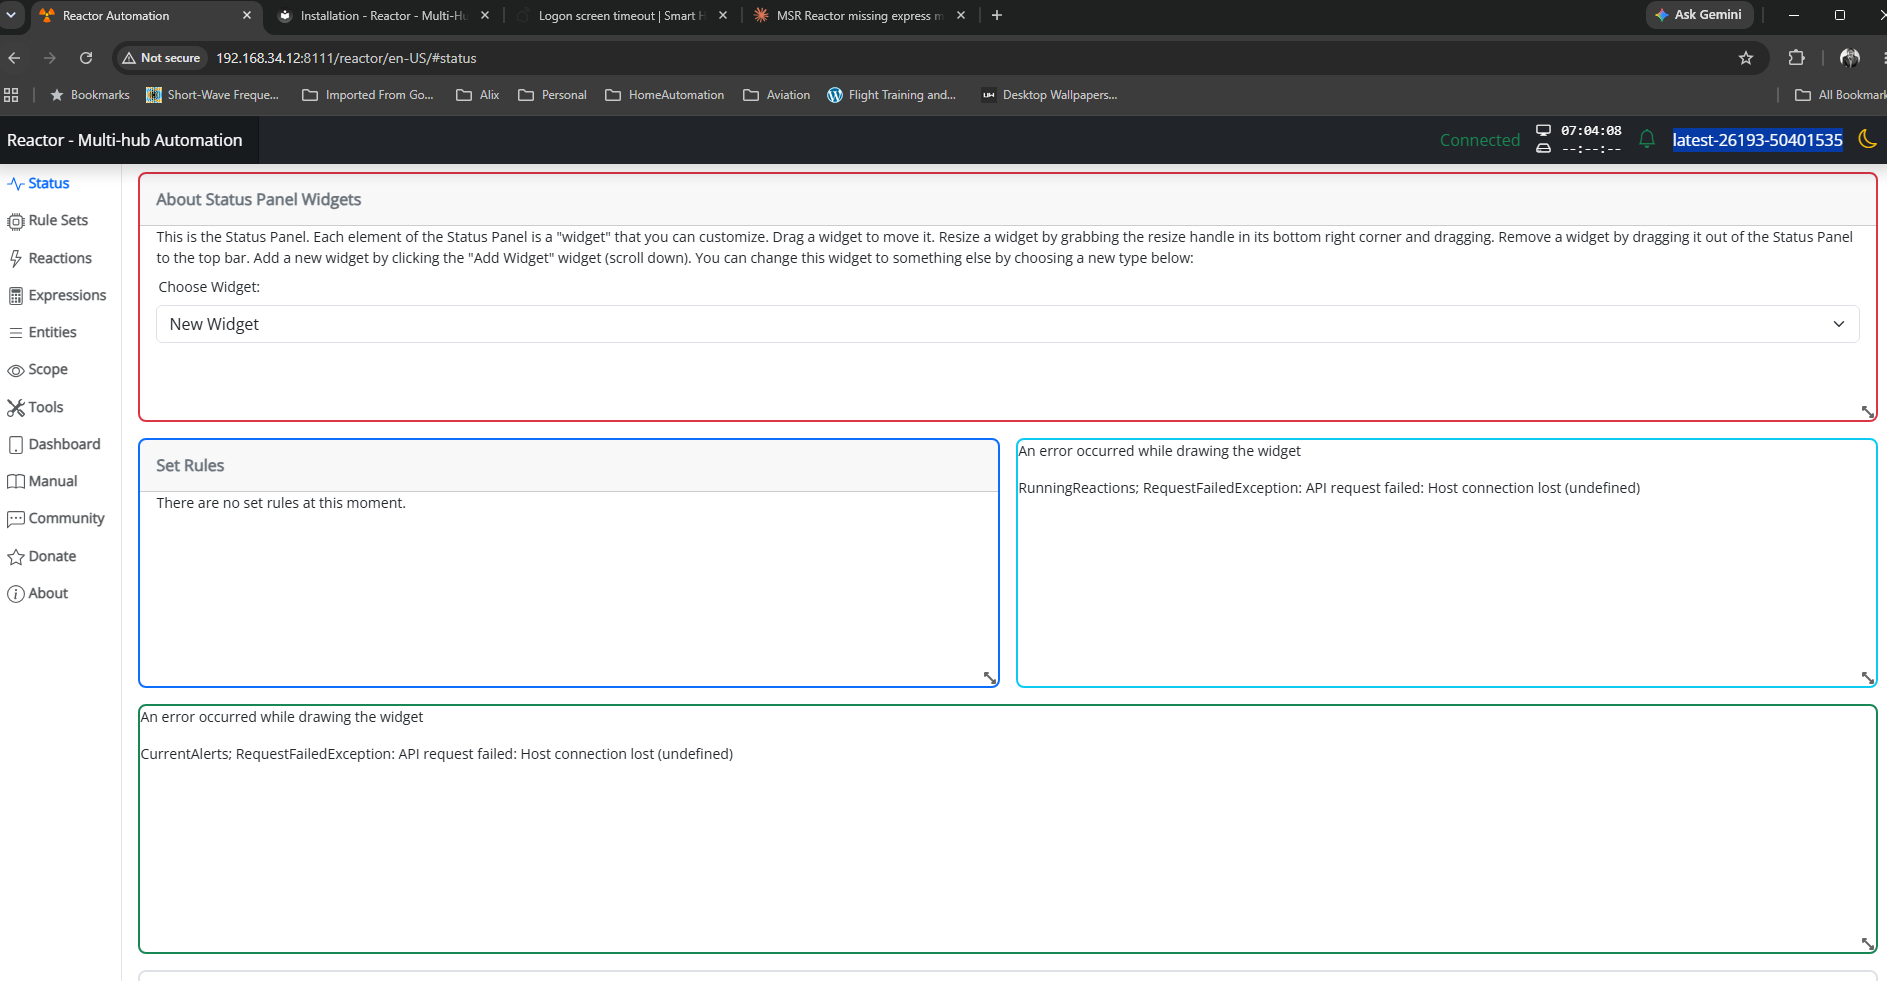
I'm trying to use MSR via reserve proxy in Synology DSM, but MSR page does not load
https://<public ip>:30000/reactor/en-US/At the same time logging page loads normally
https://<public ip>:30000/api/v1/logI thought maybe authentication was messing it up, but there was no deny entries in the log, and also disabling authentication did not make any difference. For this use case VPN is not an option (that works, but as said not an option for this particular use case).
Any ideas what could cause this? MSR build latest-26242-28d69aa8, Chrome browser
-
Do you have
baseurlset in your config?Author of Multi-system Reactor and Reactor, DelayLight, Switchboard, and about a dozen other plugins that run on Vera and openLuup.
-
Do you have
baseurlset in your config?@toggledbits yes I have
baseurl: "http://<private ip>:8111" -
Yeah, that will likely be a problem. It will try to redirect to that private IP and find itself unable. The API calls to the public IP don't need to do this, but the UI interfaces very much do. You might try putting the public IP there.
Author of Multi-system Reactor and Reactor, DelayLight, Switchboard, and about a dozen other plugins that run on Vera and openLuup.
-
Yeah, that will likely be a problem. It will try to redirect to that private IP and find itself unable. The API calls to the public IP don't need to do this, but the UI interfaces very much do. You might try putting the public IP there.
@toggledbits if I’d put public IP there, would it still work as expected when UI is used without a proxy? Also, does it accept dns name or just IPs?
Using MSR on Docker (Synology NAS), having InfluxDB, Grafana & Home Assistant, Zigbee2MQTT & ZWA-2
-
@toggledbits if I’d put public IP there, would it still work as expected when UI is used without a proxy? Also, does it accept dns name or just IPs?
@tunnus said in MSR with reverse proxy:
if I’d put public IP there, would it still work as expected when UI is used without a proxy?
That's a routing/firewall issue. Some will do it out of the box, some you have to enable it (it's often called NAT loopback, NAT hairpinning, or NAT reflection).
@tunnus said in MSR with reverse proxy:
Also, does it accept dns name or just IPs?
It should. That may be another path for you -- internal DNS resolution gives the local address, while external give the public address.
Caution all around, though. I don't build or test this for use in such proxies. I can foresee issues with access control in your scenario, because there's a high probability of extra steps needed to "see through" the proxy to the real original requesting address. If it works for you, fine, but at the moment, I'm not inclined to do more on this.